3 posts tagged with "bsi-tr-03161"
View all tags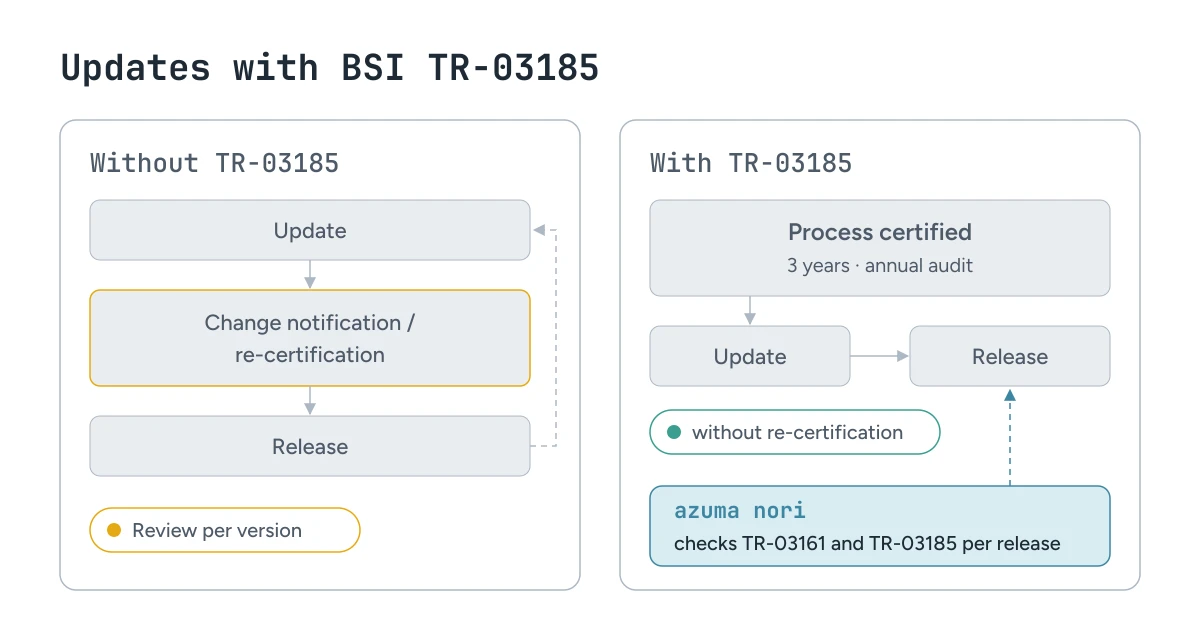
On 22 September 2026, the BSI (German Federal Office for Information Security) handed over the first certificate under BSI TR-03185 to our partner DUX Healthcare from Karlsruhe. Manufacturers who have their development process certified under TR-03185 can ship updates to a TR-03161-certified health application without having every version re-assessed.
This article explains what BSI TR-03185 requires, how the update procedure works, and why DiGA manufacturers already have a good starting point with their ISO 27001 ISMS.
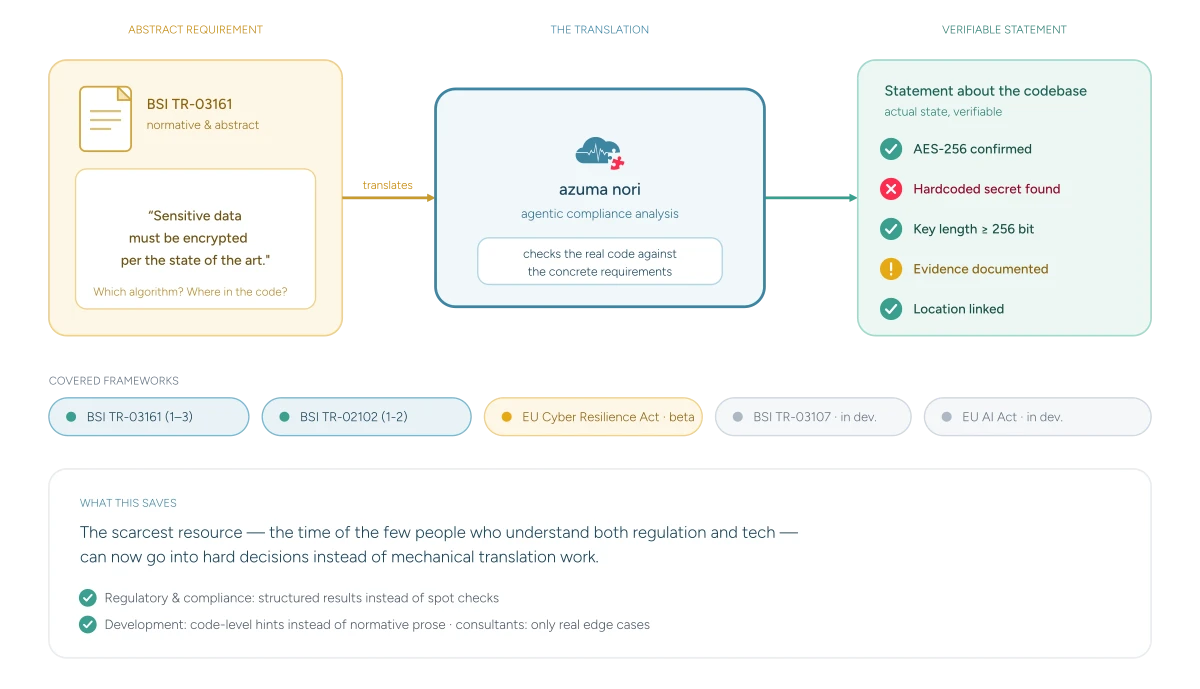
There's a translation gap between a regulatory requirement and the line of code that satisfies it. On one side stands a regulatory or compliance lead who knows BSI TR-03161 or the EU Cyber Resilience Act. On the other, a development team that wants to ship, but rarely has time to work through several hundred pages of technical guideline. Translating between the two worlds costs time, money, and patience – and is the real friction in the compliance process.
This article describes where that gap comes from, what it costs, and how azuma nori closes it by translating regulatory requirements directly into concrete, verifiable statements about the codebase.
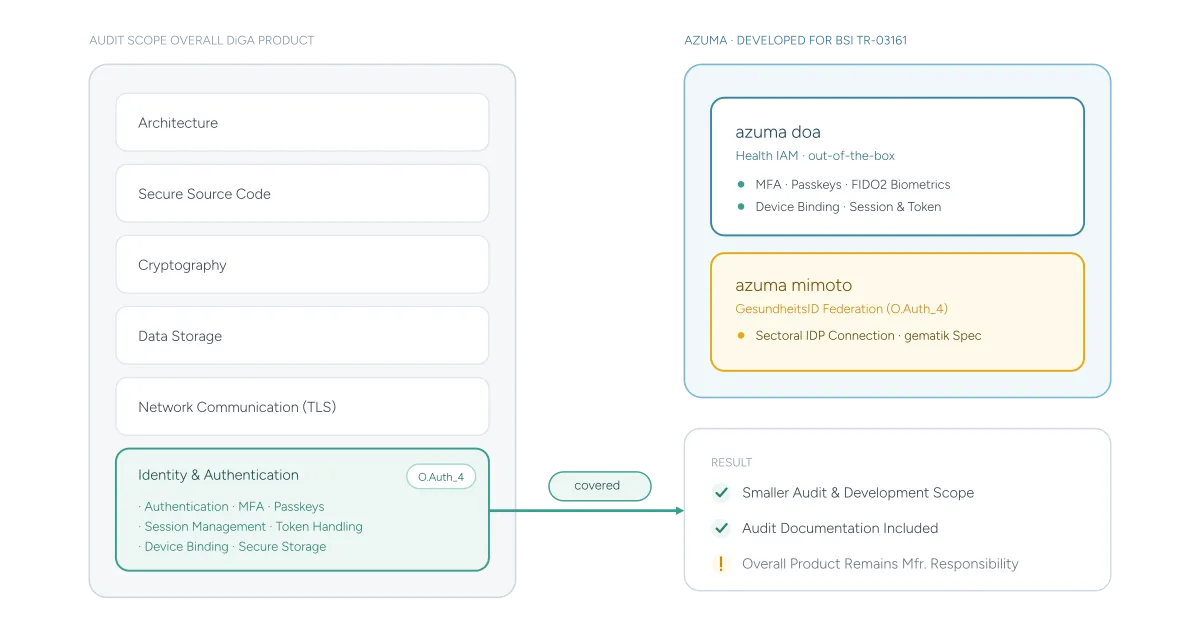
Since January 1, 2025, self-declarations are a thing of the past: DiGA manufacturers must prove compliance with data security requirements via an official certificate according to BSI TR-03161 to be included in the DiGA directory. This has turned a recommendation into a strict admission requirement – and for many teams, the critical path to reimbursement.
This article explains what the BSI TR-03161 is, what requirements it sets, how the certification works, and what specifically matters regarding authentication and identity management.