4 posts tagged with "digital-health"
View all tags
The technical documentation is complete. SOPs are approved, risk management is documented, evidence is filed. Then the review question arrives: how exactly is this security requirement implemented?
The room goes quiet. Not because nobody knows the answer, but because nobody can substantiate it in reasonable time. The quality manager wrote the chapter but has no access to the repository. The engineer knows the implementation but has never read the document. Between them sits a translation gap – and in an audit, that gap is exactly what's under discussion.
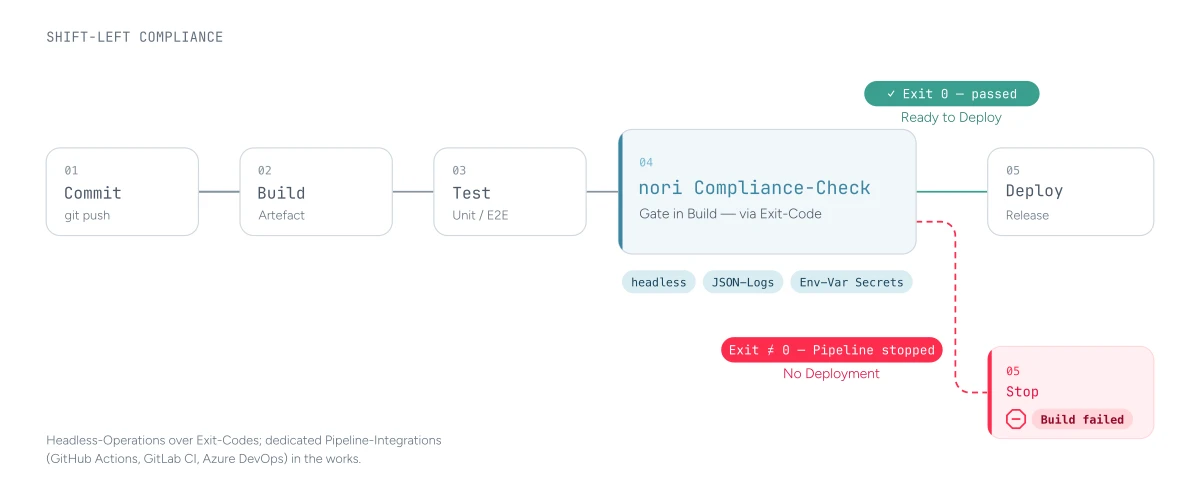
In many digital health teams, compliance is an event rather than a process: once a year, shortly before an audit or certification, someone checks where things stand. Every line of code written between two such deadlines goes unassessed until the next one – and the gaps discovered then are expensive to fix.
azuma nori supports both modes of operation: the classic gap analysis as a snapshot, and headless operation, which lets you automate the check inside your CI/CD pipeline. This article shows how to move from point-in-time to continuous compliance.
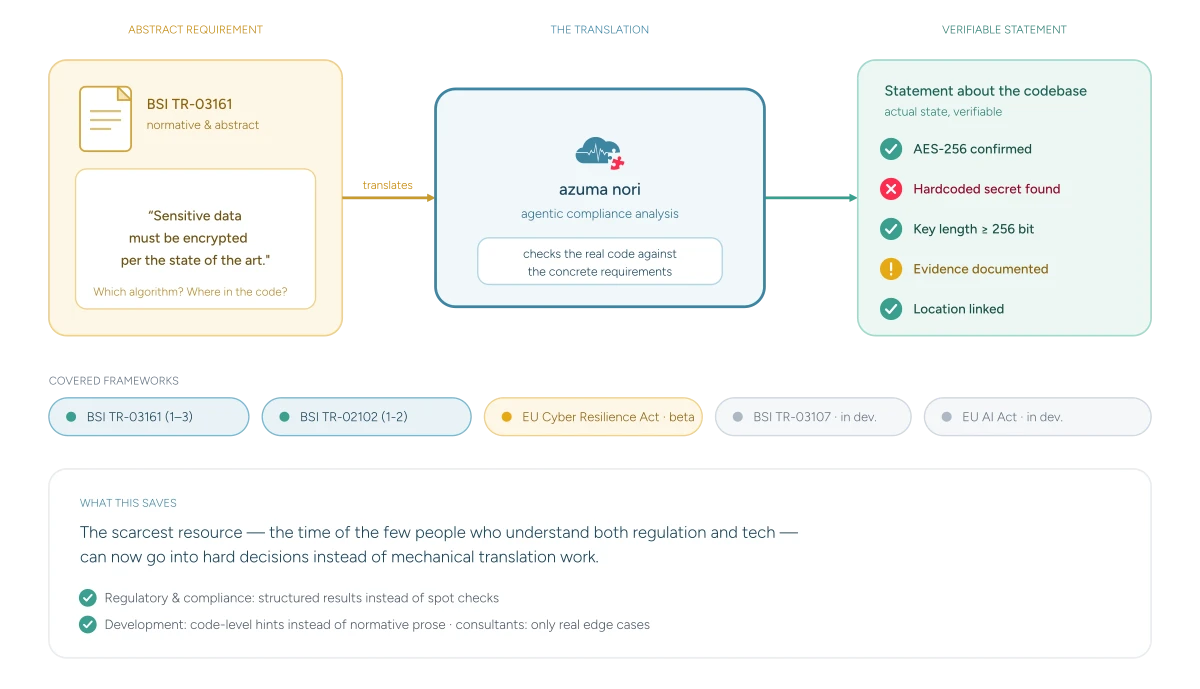
There's a translation gap between a regulatory requirement and the line of code that satisfies it. On one side stands a regulatory or compliance lead who knows BSI TR-03161 or the EU Cyber Resilience Act. On the other, a development team that wants to ship, but rarely has time to work through several hundred pages of technical guideline. Translating between the two worlds costs time, money, and patience – and is the real friction in the compliance process.
This article describes where that gap comes from, what it costs, and how azuma nori closes it by translating regulatory requirements directly into concrete, verifiable statements about the codebase.
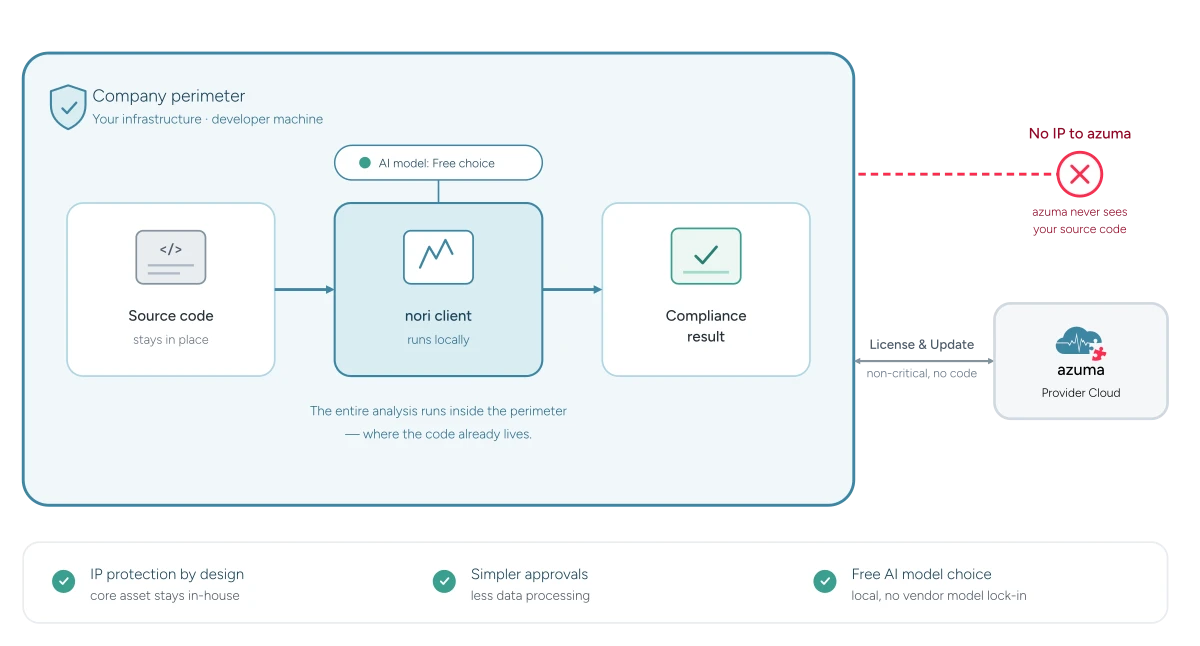
For most digital health companies, source code is the most valuable asset – and also the most sensitive one. That's exactly why it's a problem that many compliance and code-analysis tools require you to upload your code to a third-party cloud for analysis. You trade compliance for losing control over your own IP.
azuma nori takes the opposite approach: the analysis runs locally on the developer's machine, and the source code never leaves the device. This article explains why that makes a real difference, both architecturally and legally.