3 posts tagged with "iam"
View all tags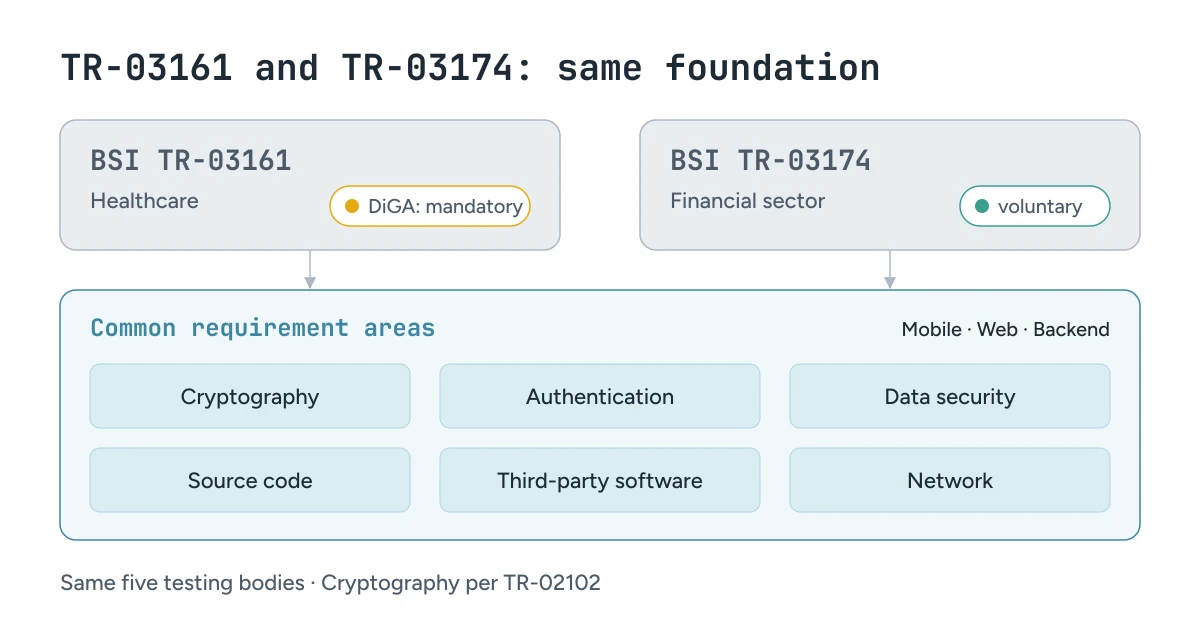
What would bother you more: an emptied bank account or an exposed patient record? Many people would instinctively say the bank account. Yet health apps have long had an established benchmark in BSI TR-03161, and for DiGAs (prescribable digital health applications in Germany) the attestation is even mandatory. The counterpart for financial apps is BSI TR-03174 "Secure Applications in the Financial Sector", at version 4.0 since June 2026.
This article explains what BSI TR-03174 requires, who it applies to, and why experience from healthcare carries over directly.
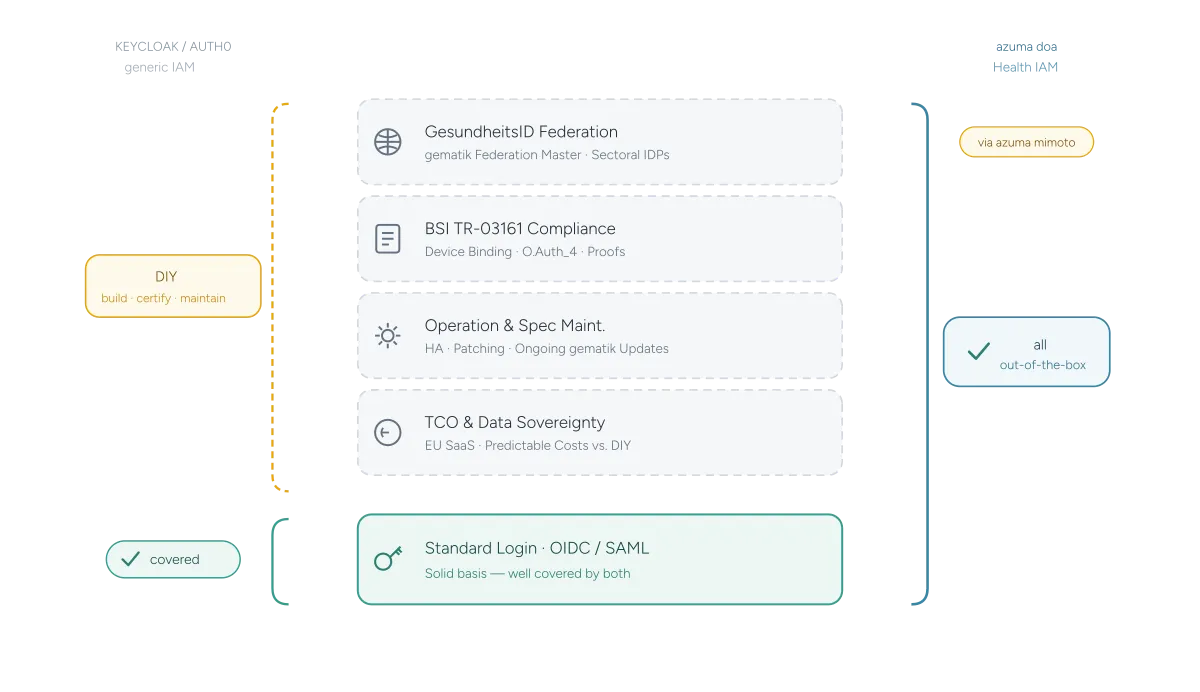
Almost every DiGA team faces the same question early on: "We know Keycloak / Auth0 – can't we just use that?" A valid consideration, as both are mature Identity & Access Management systems. The honest answer is: For the login of a standard web application, yes – for a regulated digital health application with GesundheitsID and BSI TR-03161 requirements, you will hit clearly identifiable limits.
This article categorizes what Keycloak and Auth0 do well, where they reach their limits in the healthcare context, and when a specialized Health IAM is the better choice.
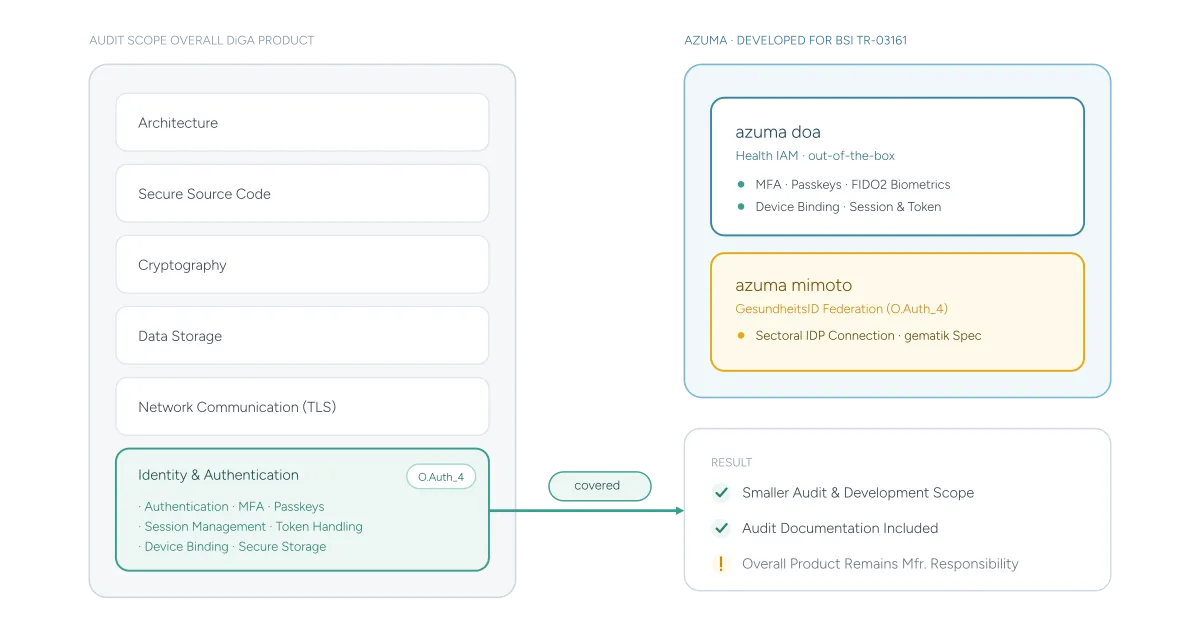
Since January 1, 2025, self-declarations are a thing of the past: DiGA manufacturers must prove compliance with data security requirements via an official certificate according to BSI TR-03161 to be included in the DiGA directory. This has turned a recommendation into a strict admission requirement – and for many teams, the critical path to reimbursement.
This article explains what the BSI TR-03161 is, what requirements it sets, how the certification works, and what specifically matters regarding authentication and identity management.